
Norseman's Technology Perspectives
Practical views on AI, cybersecurity, cloud, and edge computing from the people who build and run these systems. Norseman is an enterprise technology integrator, born from 34 years of delivery in high consequence environments, including the Department of War (DoW) and the Intelligence Community.
Federal, public sector, and commercial readers are all welcome here. Pick your audience below, or search by topic.
CMMC Phase II Is Paused. Your 800-171 Obligations Are Not.
November 10, 2026 was supposed to be the day third party CMMC certification became a condition of award for many defense contracts. It came and went without that requirement, and some suppliers are treating the pause as permission to stop spending on security and CMMC compliance. That is a costly misreading.
NASA SEWP VI Opens, NITAAC Closes, GSA Consolidates: What Federal Buyers Should Do Now
In the space of three days this fall, one major family of contract vehicles closed to new orders and another opened. CIO-SP3 and CIO-CS took their last new orders on October 29, 2026, and NASA SEWP VI opened on November 1. Meanwhile, GSA is consolidating governmentwide buying and the FAR overhaul is rewriting the rules.
Post Quantum Starts With an Inventory You Do Not Have
Every post quantum cryptography plan starts with one question: where do we use cryptography today? Most organizations, federal agencies included, cannot yet answer it. In 2026 that question gained deadlines.
After the VMware Renewal: Stay, Shrink or Switch
Most VMware customers have now seen at least one Broadcom era renewal quote, and many did not like what they saw. The pressure to "just leave" for one of the VMware alternatives is real, but leaving takes longer and costs more than many teams expect. The better question is not whether to leave VMware.
The 12 Month Server: Planning a Refresh When Lead Times Outlast the Budget Year
Your next server may not arrive in the fiscal year you pay for it. The 2026 memory shortage, which many buyers call the RAM shortage, pushed some infrastructure lead times to 12 months or longer. On top of that, the quote you received last week may already have expired. That is a planning problem more than a purchasing problem.
Designing AI for the Places the Cloud Does Not Reach
Most AI software is built on an assumption that quietly fails offshore, underground, downrange, and inside accredited enclaves. Here is how to build for the other case, what it takes to field it, and the seven questions that reveal whether a vendor has actually operated disconnected.
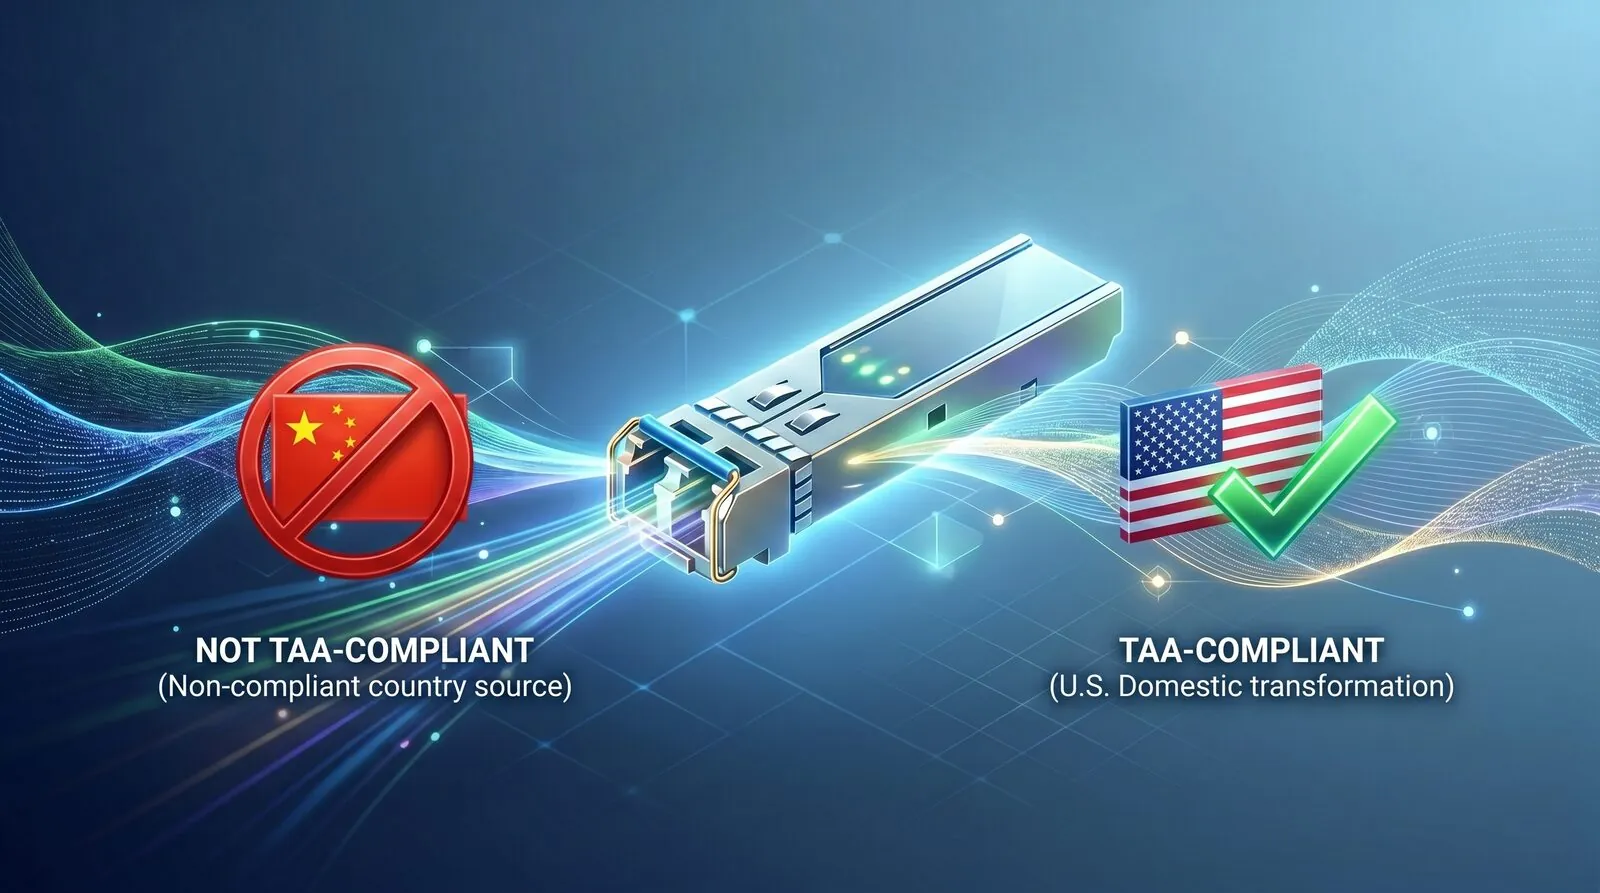
The Optics Play: TAA-Compliant Third-Party Transceivers Without the Support Risk
Third-party optics can save federal programs seven figures without sacrificing TAA compliance or OEM support, if you understand the Magnuson-Moss Warranty Act, the "substantial transformation" rule, and the emergency-kit strategy. Here's the field guide for acquisition and program teams.
Beyond the Hype: The Right Way to Implement AI-Supported Application Development
AI coding tools promise unprecedented speed. But for federal, defense, and enterprise organizations, the rush to adopt has collided with security, compliance, and infrastructure readiness. Here's the blueprint for making it work.
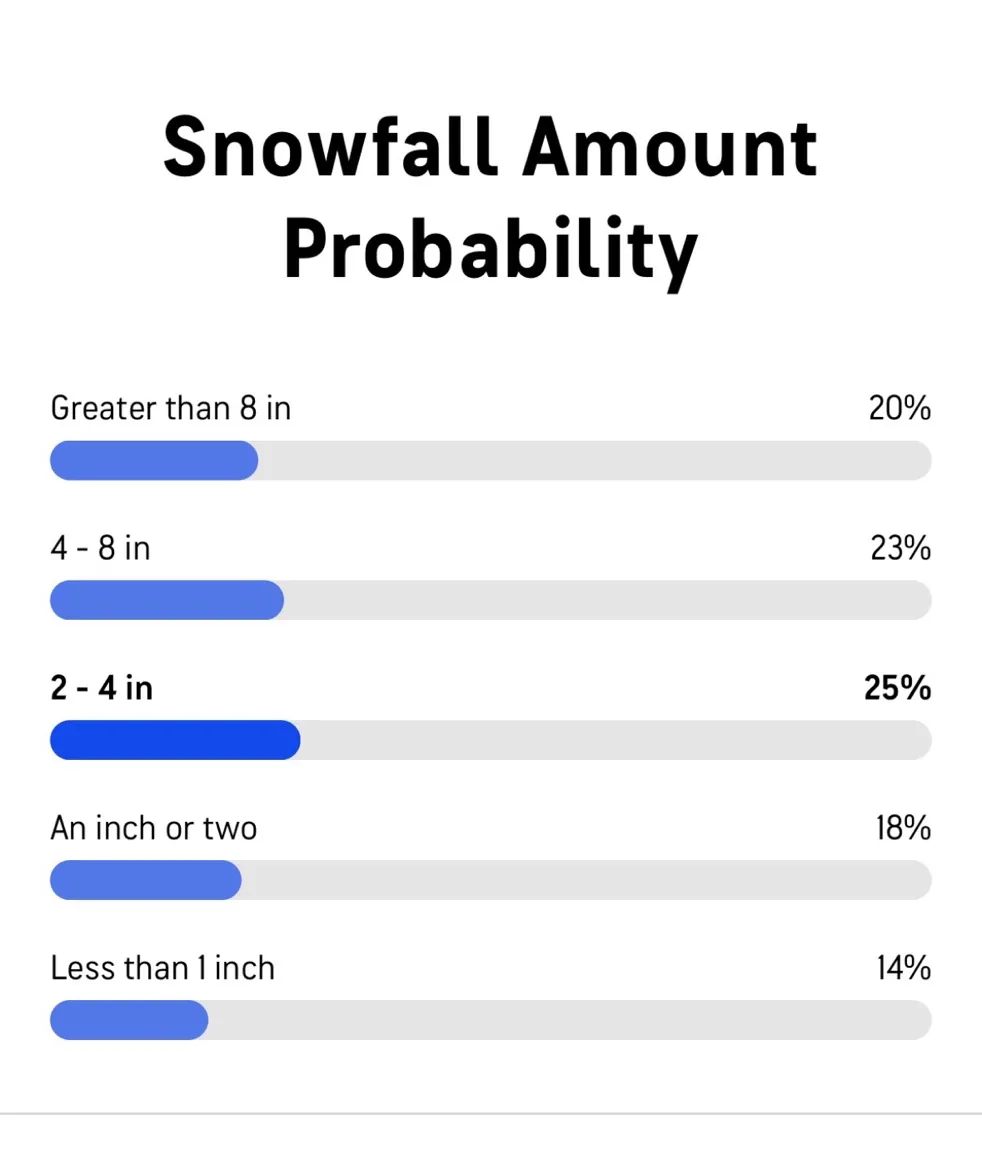
Your Data Shouldn't Sound Like a Weather Forecast
Most organizations invest in AI and get probability: five possible answers instead of one they can act on. Norseman's Applied AI practice engineers the full stack from data ingestion to decision support, narrowing the spread and giving leaders the clarity they need.
Virtual Machine Hosting: Choosing the Right Cloud for Your Workload
The commercial VM hosting market has never been more competitive, or more confusing. AWS, Azure, Google Cloud, Oracle, and a growing tier of specialized providers each make compelling claims. This guide cuts through the noise with a workload-first framework to help enterprise IT leaders make the right call.
Securing the Financial Supply Chain: Proactive C-SCRM in FinTech
The modern financial ecosystem relies on an intricate web of third-party vendors and open-source software, making Cyber Supply Chain Risk Management (C-SCRM) paramount. Integrating supply chain illumination platforms alongside robust cloud and container security creates a zero-margin-for-error security environment.
IT Transformation at the Edge: Accelerating Healthcare and Pharma R&D
Healthcare and pharmaceutical organizations generate massive datasets that must be processed with absolute precision and speed. Edge computing allows organizations to process critical data closer to the source, whether in an ICU or a remote research facility, reducing latency and delivering real-time analytics for rapid R&D.
Unrelenting Automation: Driving the Retail Supply Chain Forward
The retail landscape is shifting rapidly, and defending market position requires a supply chain that never hesitates. Defense-grade service management and automated workflows eliminate operational bottlenecks and optimize inventory flow with military precision.
Defending the Network: DevSecOps in Modern Telecommunications
Telecommunications providers are the backbone of global connectivity, making their networks prime targets in adversarial environments. Embedding DevSecOps directly into the software development lifecycle ensures security is a continuous, automated process, not an afterthought.
Elevating Aviation: AI and Machine Learning in Flight Logistics
Aviation demands zero-margin-for-error operations where every variable must be calculated and controlled. AI, ML, and Deep Learning are redefining how the aviation industry approaches predictive maintenance, route optimization, and fleet management.
The Operational Advantage: AI-Driven Enterprise Transformation
Leading the market requires executing complex operations without hesitation. Modern enterprises must adopt AI-driven solutions to automate critical workflows, generate intelligent responses to market demands, and maintain a proactive stance in rapidly evolving markets.
Responsible AI in Government Operations
AI is transforming government operations, but rapid adoption without strong safeguards risks exposing sensitive data. At Norseman, we help agencies deploy AI responsibly: secure-by-design, privacy-focused, and mission-ready.
Federal IT Modernization: Riding the Wave or Being Pulled Under?
The federal IT landscape is undergoing a massive shift: legacy systems are being sunset, contracts are consolidating, and agencies are expected to deliver faster, more resilient digital services with fewer resources. IT modernization isn't just about cloud migration anymore.
Trusted AI: Explainable, Auditable, Resilient
AI is everywhere. But in national security, 'everywhere' isn't good enough. What matters is trusted AI: explainable, auditable, and resilient under adversarial conditions. Black-box algorithms won't cut it when lives or missions are on the line.
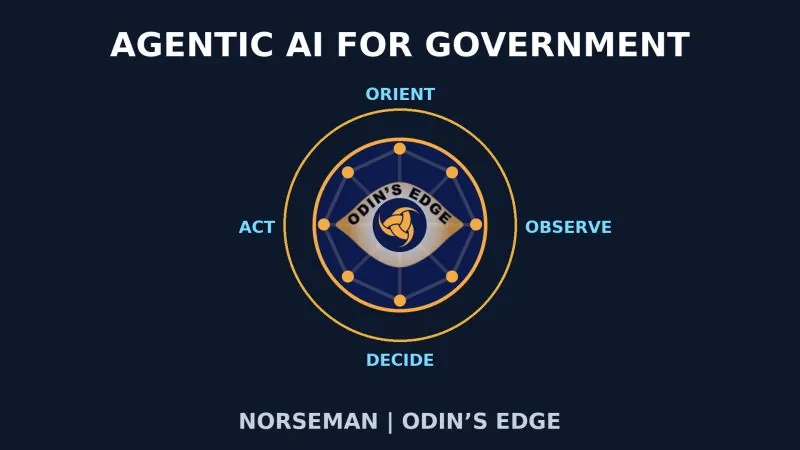
Agentic AI for DoD: An OODA Loop That Doesn't Sleep
Agentic AI in DoD terms is an OODA loop that doesn't sleep. It's not about cloning yourself to execute poor procedures faster. It's about compressing the decision cycle and proving why each step happened.
Cyber Resilience Isn't a Press Release
Another 'oops' from a big-name vendor. When corporate giants shrug off trust, it's the government networks and cyber defenders left holding the bag. At Norseman, we don't shrug trust. We pair with Rubrik to lock down data with zero-trust security and ensure rapid recovery.
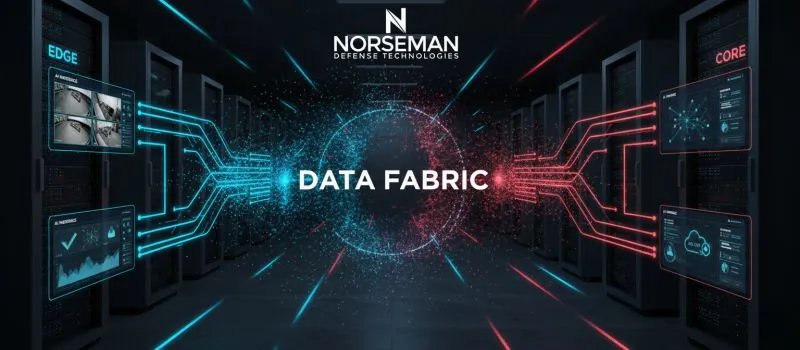
Building a Real Data Fabric from Edge to Core
A real data fabric functions as a streaming contract bridging edge and core operations. Ensuring reliable event publication at the edge is crucial to the accuracy of AI processes, and the key is Confluent-backed event streaming with governance built in.
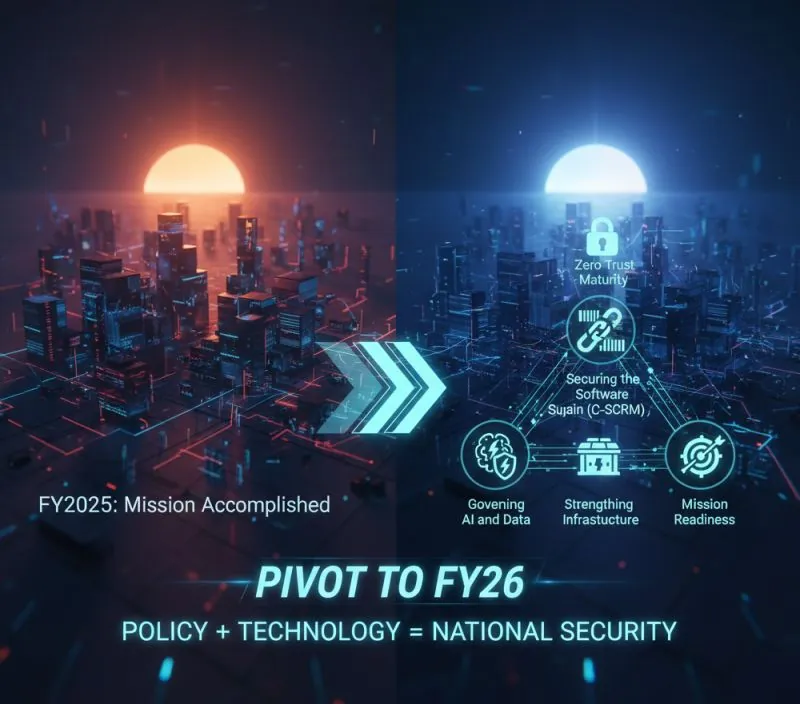
Pivot to FY26: Policy + Technology = National Security
As FY25 draws to a close, the intersection of policy and technology will shape national security for the year ahead. Zero Trust maturity, software supply chain security, AI governance, and critical infrastructure resilience are the four pillars agencies must address.
Zero-Copy Data Architecture at the Edge
Every extra data copy adds risk, latency, and cost. That's why Norseman leads with zero-copy data architectures at the edge, built and implemented on Odin's Edge. If your edge strategy still depends on staging folders and temp disks, you're leaving time, security, and dollars on the table.